What Is a SOC Analyst? Roles, Skills, Salary & Career Path Explained
Oct 15, 2026
What Is a SOC Analyst?
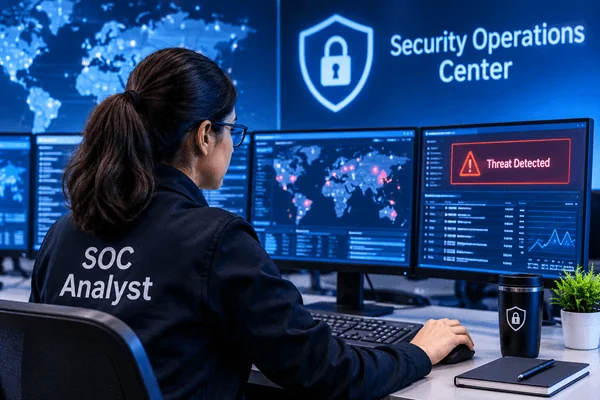
A SOC analyst is a security professional who watches over an organisation's systems, networks and data round the clock. They spot suspicious activity, investigate alerts and act quickly to stop attacks. At Hacker School, we train learners for this exact role, so this blog explains what the job really involves.
Roles and Responsibilities of a SOC Analyst
Every Security Operations Centre runs on a team that shares the load. Here is what a typical analyst handles in a day, and what you can expect to do once you join one.
Continuous Security Monitoring
Analysts watch dashboards, alerts and network traffic all day. The goal is to catch unusual behaviour before it turns into a serious incident for the business.
Alert Triage and Prioritisation
Not every alert is dangerous. Analysts sort them by severity, separate false alarms from real threats and decide which ones need attention first.
Log Collection and Analysis
Servers, firewalls and applications create huge volumes of logs. Analysts read through them to find patterns, errors and signs of unauthorised access.
Incident Detection
When an alert looks genuine, the analyst confirms it by checking related events, user activity and system behaviour before raising an incident.
Incident Response
Once an attack is confirmed, analysts contain it, remove the cause and help systems return to normal with as little damage as possible.
Threat Hunting
Analysts do not wait for alerts alone. They actively search networks for hidden threats that automated tools may have missed.
Vulnerability Tracking
They keep an eye on weaknesses in software and systems, and work with IT teams so that important fixes are applied on time.
Malware Investigation
Suspicious files and links are checked in safe environments so the team understands what the malware does and how to stop it.
Digital Forensics Support
Analysts preserve evidence, record timelines and support deeper investigations after a breach has taken place.
Reporting and Documentation
Every incident is written up clearly. Good reports help managers, auditors and fellow analysts learn from what happened.
Team Coordination
SOC work is never solo. Analysts pass information across shifts, escalate to senior members and talk to other departments during incidents.
Key Skills of a SOC Analyst
Technical knowledge matters, but so do habits and attitude. A good analyst combines both. Here is what employers usually look for.
Networking Fundamentals
Knowing how TCP/IP, DNS and common protocols work makes odd traffic easy to notice.
Operating System Knowledge
Comfort with Windows and Linux helps you read system events and trace what an attacker did.
Log Analysis
You should be able to read logs quickly and pick out the lines that actually matter.
SIEM Tool Handling
Tools like IBM QRadar and Splunk collect events in one place, and analysts must know how to search and tune them.
Understanding of Cyber Threats
Knowing common attack types, indicators of compromise and attacker methods helps you recognise danger early.
Incident Handling
You need a clear, step-by-step way to deal with an attack without panicking.
Malware Basics
A basic idea of how malware spreads and behaves helps during investigations.
Cloud Security Awareness
Many companies now run workloads on the cloud, so cloud monitoring is becoming a regular part of the job.
Scripting Basics
Simple scripts save time on repeated tasks, though heavy coding is not compulsory.
Analytical Thinking
Good analysts connect small clues and ask the right questions before concluding.
Attention to Detail
One missed line in a log can hide an entire attack, so careful reading counts.
Communication Skills
You must explain technical issues in simple words to managers and teammates.
Stress Handling
Incidents rarely arrive at a convenient time. Staying calm under pressure is a real strength.
How Can I Become a SOC Analyst?
Many people ask this, and the good news is that the path is clear. Follow these steps to build a solid base.
Learn IT and Networking Basics
Start with how computers, networks and the internet work. Without this base, security topics feel confusing.
Understand Core Security Concepts
Study threats, vulnerabilities, attacks and defences. Know what confidentiality, integrity and availability mean in daily practice.
Get Hands-On With Tools
Reading is not enough. Practise on SIEM platforms, log sources and incident scenarios, ideally in a lab where mistakes cost nothing.
Join a Structured Training Programme
A proper course saves months of confusion. The EC-Council programme at our institute, which is the EC Council Certified SOC Analyst course, covers monitoring, detection and response in a logical order.
Earn a Recognised Certification
A credential proves your knowledge to employers. It also pushes you to finish the syllabus instead of leaving it half done.
Build Practical Experience
Try internships, home labs or capture-the-flag events. Real exposure makes interviews far easier.
Apply for Entry-Level Roles
Look for Tier 1 SOC analyst or security monitoring openings. Many successful analysts started exactly there.
SOC Analyst Career Path
A SOC role is a starting point, not a dead end. With experience, the growth options are wide and rewarding.
Tier 1 SOC Analyst
This is where most people begin. You monitor alerts, do first-level checks and escalate real incidents to senior colleagues.
Tier 2 SOC Analyst
Here you handle confirmed incidents in depth, run investigations and guide junior members through trickier cases.
Tier 3 SOC Analyst or Threat Hunter
At this level, you hunt threats proactively, study malware and shape detection rules for the whole team.
SOC Manager
With leadership skills, you can manage the team, plan shifts, track metrics and report to senior management.
Why SOC Analysts Are Important
Companies lose money, trust and customers when attacks succeed. Analysts keep that risk low. Their value shows up in many ways.
- Early threat detection – they spot attacks before real damage happens.
- Faster response – trained analysts cut down the time between an attack and its containment.
- Data protection – customer and business data stays safer under constant watch.
- Business continuity – quick action means systems stay up and work continues.
- Compliance support – logs and reports help companies meet audit and legal requirements.
- Better security decisions – incident data shows management where the real weaknesses lie.
- Customer trust – clients stay loyal to companies that handle security seriously.
Average Compensation for a SOC Analyst
Pay depends on city, company and skill level. In India, freshers usually start at roughly ₹3 to ₹6 lakh per year. With two to four years of experience, many analysts earn around ₹8 to ₹15 lakh. Senior analysts and managers in large firms can go well beyond that. A recognised SOC analyst certification and strong tool experience often help candidates negotiate a better offer. Figures vary by employer, so treat them as a general range.
SOC Analyst Certification
A SOC analyst certification tells employers that you understand real security operations, not just theory. Among the options available, the Certified SOC Analyst CSA programme from EC-Council is built especially for people who want to start or grow in a SOC team. It covers eight modules, from security operations and log management to incident response, forensics and cloud SOC.
Our training for this credential has several practical advantages.
- 60+ hours of live, instructor-led sessions
- 50 to 60 hours of cloud lab access for practice
- Recorded sessions, so a missed class is never a worry
- Technical support whenever you get stuck
- Exam voucher included, with a single attempt
- No prerequisites so that beginners can join confidently
- Fee payable in two instalments
The EC Council Certified SOC Analyst exam is taken after training, and the lab hours make sure you are comfortable with tools before test day.
Sample SOC Analyst Job Description
Here is a simple example of what employers often post.
Job Title – SOC Analyst (Tier 1)
Role Summary: The company seeks a motivated analyst to monitor security alerts, investigate incidents and support the response team in a 24x7 environment.
Key Responsibilities
- Monitor SIEM dashboards and security alerts in real time
- Triage alerts and escalate genuine incidents
- Analyse logs from firewalls, servers and endpoints
- Document incidents and update the ticketing system
- Follow response playbooks during security events
- Coordinate with IT teams on remediation
Requirements
- Basic knowledge of networking, operating systems and security concepts
- Familiarity with SIEM tools such as QRadar or Splunk
- Good communication and reporting skills
- Willingness to work in rotational shifts
- A relevant certification is preferred
Benefits of Becoming a SOC Analyst
The role is demanding, but it pays back in many ways. Here is why many people choose it.
Strong Job Demand
Every company with an online presence needs security monitoring, so openings keep coming.
Good Starting Entry Point
You can enter cybersecurity without years of prior experience.
Clear Growth Path
Promotions from Tier 1 to Tier 3 and management are well defined.
Attractive Salary Growth
Pay rises steadily as your skills and responsibilities grow.
Hands-On Learning Every Day
No two shifts look the same, so you keep learning real skills.
Exposure to Many Tools
You work with SIEM, EDR, firewalls and threat intelligence platforms.
Value in Global Markets
SOC skills are recognised across countries, which opens remote and overseas options.
Pathway to Specialisation
Later, you can move towards forensics, threat hunting, red teaming or cloud security.
Meaningful Work
You protect real people and real businesses from harm.
Credential Support
Earning the Certified SOC Analyst CSA credential adds weight to your profile from day one.
Common SOC Analyst Interview Questions
Interviewers usually test both basics and thinking style. Prepare for questions like these.
- What is the difference between an event, an alert and an incident?
- How would you handle a phishing email reported by an employee?
- What is a SIEM and how does it work?
- Explain the difference between a true positive and a false positive.
- What are indicators of compromise?
- How do you prioritise multiple alerts at once?
- What steps do you follow in incident response?
- Can you explain a brute-force attack and how to detect it?
- Which log sources would you check for a suspected malware infection?
- How do you keep up with new threats?
If you have completed a recognised
SOC analyst certification, mention the labs and scenarios you practised. Real examples, even from training, always sound stronger than memorised definitions.
SOC Analyst FAQs
1. Do I need coding skills to become a SOC analyst?
Not compulsory. Basic scripting helps with automation, but most entry-level roles focus on monitoring, log reading and incident handling.
2. Can a fresher become a SOC analyst?
Yes. With proper training, lab practice and a good certification, freshers regularly get Tier 1 roles. Our course needs no prerequisites.
3. How long does it take to prepare?
With a structured programme of 60+ live hours and regular lab practice, most learners feel ready within a few months.
4. What does the Certified SOC Analyst programme cover?
It spans eight modules, including log management, incident detection and triage, proactive threat detection, incident response, forensics, malware analysis and cloud SOC.
5. Is the exam included in the course fee?
Yes. The EC Council Certified SOC Analyst exam voucher is included with a single attempt. The course costs ₹34,000 plus GST, and payment can be made in two instalments.
6. Are classes available online and offline?
Yes. Batches run live online and offline in Bangalore and Hyderabad, with upcoming starts in November and December 2026.
Not Quite Ready for Role-Specific Content?
If you are still deciding, that is perfectly fine. Talk to the team at Hacker School, attend a free demo and see how the classes and cloud labs work before you commit. Visit our website to check batch dates and request a callback.